iTranslated by AI
Investigating IAM Policy Settings for Amazon Q Developer (AWS Chatbot) and Slack Integration




Introduction
By linking Amazon Q Developer (formerly AWS Chatbot) with Slack, you can receive AWS notifications in Slack channels.
When setting up this link, authentication with a Slack workspace is required for the first time. I wanted to perform that authentication with a specific IAM user, so I investigated the IAM policy required for that authentication process.
This article describes the results of my investigation into the IAM policy required for the initial Slack authentication of Amazon Q Developer (formerly AWS Chatbot).
What is not covered
Confirmation of notifications to Slack after the initial Slack authentication is not covered in this article.
Goal
- Understand the IAM policy required for the initial Slack authentication of Amazon Q Developer (formerly AWS Chatbot).
- Confirm that under Amazon Q Developer > Slack workspaces > Workspace details > Status, the state is shown as
Enabled.
Conclusion
The following IAM permission policy successfully allowed the initial integration between Amazon Q Developer (AWS Chatbot) and Slack.
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Effect": "Allow",
            "Action": [
                "chatbot:CreateSlackChannelConfiguration",
                "chatbot:DescribeSlackChannels",
                "chatbot:DescribeSlackChannelConfigurations",
                "chatbot:DescribeSlackWorkspaces",
                "chatbot:GetSlackOauthParameters",
                "chatbot:RedeemSlackOauthCode",
                "iam:ListRoles"
            ],
            "Resource": "*"
        }
    ]
}
I have documented what I did in a Zenn scrap.
What I Investigated
Since AWS Chatbot was recently renamed to Amazon Q Developer, I checked if the action names had also changed and confirmed that the IAM permissions do not seem to have been affected.
- Reference 1: https://docs.aws.amazon.com/chatbot/latest/adminguide/service-rename.html#rename-not-changing
- Reference 2: https://aws.amazon.com/jp/blogs/news/aws-chatbot-is-now-named-amazon-q-developer/
1. Creating the Policy
I listed the following actions as they seemed necessary.
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Effect": "Allow",
            "Action": [
                "chatbot:CreateSlackChannelConfiguration",
                "chatbot:DescribeSlackChannels",
                "chatbot:DescribeSlackWorkspaces",
                "chatbot:GetSlackOauthParameters",
                "chatbot:RedeemSlackOauthCode"
            ],
            "Resource": "*"
        }
    ]
}
2. Slack Integration Settings
- Log in to the AWS Management Console
- Navigate to Amazon Q Developer in chat applications
- Select Chat clients > Slack
- Click the "Configure client" button

3. Authentication with Slack Workspace
When requested for permission to access the Slack workspace, select "Allow".

4. Error Occurrence and Cause
I confirmed that the status under Workspace details > Status showed as Enabled.
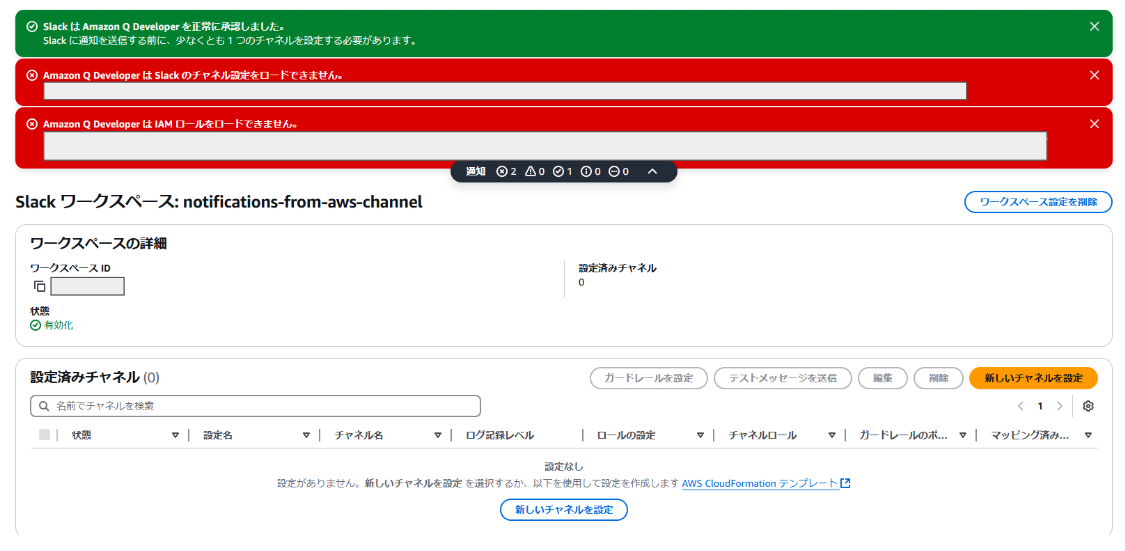
However, as shown in the image above, the following two errors occurred:
Amazon Q Developer cannot load Slack channel configurations.
User: arn:aws:iam::~~:user/test-notificate-slack-channel is not authorized to perform: chatbot:DescribeSlackChannelConfigurations on resource: arn:aws:chatbot:us-east-2:~~

Amazon Q Developer cannot load IAM roles.
User: arn:aws:iam::~~:user/test-notificate-slack-channel is not authorized to perform: iam:ListRoles on resource: arn:aws:iam::~~:role/aws-service-role/management.chatbot.amazonaws.com/ because no identity-based policy allows the iam:ListRoles action
5. Correcting the Policy
Based on the error messages, it seemed that the following two actions were missing, so I updated the IAM policy.
- chatbot:DescribeSlackChannelConfigurations
- iam:ListRoles
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Effect": "Allow",
            "Action": [
                "chatbot:CreateSlackChannelConfiguration",
                "chatbot:DescribeSlackChannels",
                "chatbot:DescribeSlackChannelConfigurations",
                "chatbot:DescribeSlackWorkspaces",
                "chatbot:GetSlackOauthParameters",
                "chatbot:RedeemSlackOauthCode",
                "iam:ListRoles"
            ],
            "Resource": "*"
        }
    ]
}
6. Re-verification
After applying the corrected policy and performing the Slack integration settings again, no errors were displayed, and the status was Enabled.
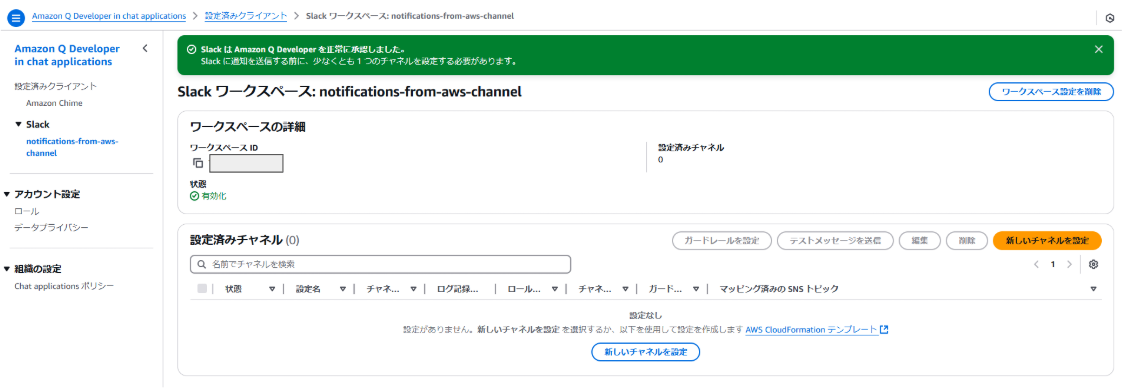
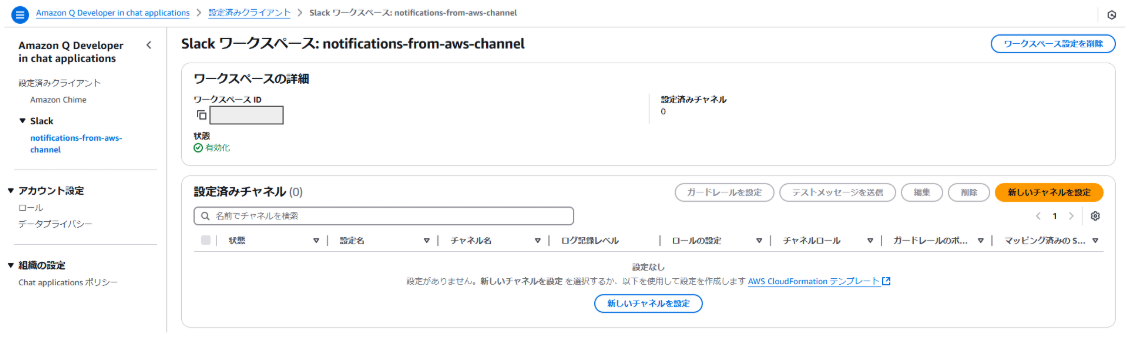
Just to be sure, I reopened the Amazon Q Developer in chat applications console and confirmed that the status of the target Slack workspace was indeed Enabled.
Discussion